Commerce and specialist fraud workflows: assign the right evidence
Connect financial, claim, identity and specialist cases without equating their evidence or operational responsibilities.
Summarize with AI
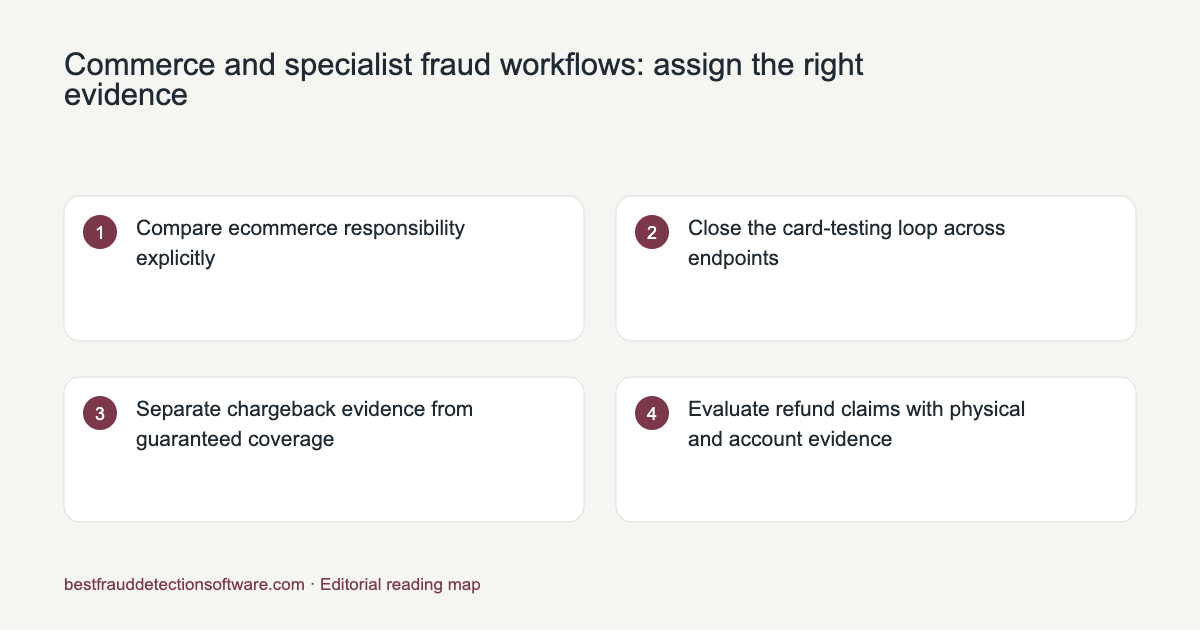
Compare ecommerce responsibility explicitly
Stripe Radar applies payment rules; Sift offers a fraud platform; Signifyd spans account and commerce protection with contractual terms; visitor-risk tools add session context. Verify guest checkout, gateway, review and refund integration. Financial guarantees differ from detection output. A useful pilot protects one cohort and measures legitimate approvals and mature loss together, rather than assuming a script install produces a ninety-day improvement.
Reference: Sift: payment and account products.
Close the card-testing loop across endpoints
Stripe describes card testing through setup or payment attempts, with failed authorizations, small payments and repeated errors as signals. Protect backend creation and retry paths with related-entity velocity, supported payment integration and secret-key security. IP filtering alone is insufficient. Use idempotent writes. Authorized test mode requires provider test data rather than probing real stolen card validity.
Reference: Stripe: protect yourself from card testing.
Separate chargeback evidence from guaranteed coverage
Device and access history can connect a disputed order to its session, while fulfillment and communication provide other evidence. Issuer processes and deadlines remain relevant. A chargeback guarantee transfers defined eligible loss under contract; a risk score does not. Preserve the original decision and outcome. No generic fraud API can promise every dispute win or removal of every TC40 report.
Reference: Stripe: how disputes work.
Evaluate refund claims with physical and account evidence
Join claimant, order, delivery, inspection and related claims before deciding. Device links may reveal repeated identities without proving item condition. Stripe documents partial refunds, original-method destinations and dispute interactions. Use a single ledger and reconcile pending or failed operations. Measure honest claimant delay and reversal alongside abuse prevented, so tighter restrictions do not simply hide legitimate losses.
Reference: Stripe: refunds.
Protect gift-card balance and redemption separately
Enumeration repeatedly probes codes or balances. Limit attempts across sessions, reduce informative failures and enforce server authorization. Atomic balances and idempotent writes prevent duplicate spending or grants. Preserve safe references rather than full codes in logs. A network or bot tool adds resistance while the application ledger determines whether the value movement itself is authorized.
Reference: OWASP: Authorization Cheat Sheet.
Map BNPL to its own actors and outcomes
BNPL can include provider account creation or login and repayment acceptance, as Stripe documents. Join that outcome to the merchant order and refunds. Device evidence helps assess session risk while the provider owns financing decisions. A good IP or device score does not establish creditworthiness. Clarify who owns eligibility, customer communication and each disputed outcome.
Reference: Stripe: buy now, pay later payment methods.
Separate synthetic identity from repeated accounts
The Federal Reserve defines synthetic identity fraud as fabricating a person or entity from combined personal information for dishonest gain. Multiple accounts can instead belong to a real person exploiting policy. Use identity proofing for claimed-person evidence and device relationships for continuity. A browser hash cannot authenticate documents, prove a legal identity or establish one-human uniqueness.
Reference: Federal Reserve: synthetic identity payments fraud.
Allow for legitimate travel behavior
Travel customers roam, use privacy services and book for others. Connect booking details, device continuity and payment confirmation, then review high-value changes and refunds. Separate availability scraping from fraudulent booking. A location mismatch alone does not establish deception. Keep one booking reference through supplier handoffs and evaluate the effect on genuine travelers alongside confirmed loss.
Reference: OWASP: Authentication Cheat Sheet.
Protect scarce ticket allocation through state
Ticket scalping can involve automation, many accounts and prohibited resale. Combine a controlled queue, purchase entitlements, account links and atomic reservations. Use idempotency for retries. Transfer policy defines permitted resale; a fingerprint cannot make a ticket universally resale-proof. Preserve legitimate group-buying and accessibility paths, and protect account recovery so existing tickets are not transferred through takeover.
Reference: OWASP: automated threats to web applications.
Evaluate voice security on telecom evidence
Caller-risk products use number, call and appropriate authentication signals. RFC 8224 describes signed SIP identity information, which does not prove honest intent. Browser audio fingerprinting measures an environment rather than identifying a caller. If support connects voice and web journeys, authenticate the owner and preserve separate evidence sources. Do not infer the most accurate robocall provider from an unrelated device-risk benchmark.
Reference: IETF: RFC 8224 and current status.
Use specialist takedown workflows for external impersonation
Fake apps, domains and social profiles require monitoring, evidence and platform-specific reports. Capture exact identifiers, timestamps and rights evidence; track the provider response. Google's legal-removal process is one documented route. A browser-risk API on your service cannot remove a counterfeit seller elsewhere. Compare monitoring coverage and evidence requirements rather than treating external removal as a byproduct of visitor scoring.
Reference: Google: report content by product and legal or policy route.
Worked example: One customer journey creates several loss cases
Hypothetical example: a compromised account buys goods, requests a refund and later disputes the charge. Connect the events under stable references without counting them as three unrelated prevented losses. Preserve access, order, claim and issuer evidence. Assign owners for containment, customer recovery and financial reconciliation, with clear correction and reporting rules.
| Event | Primary owner | Evidence |
|---|---|---|
| Takeover | Identity/security | Access and owner control |
| Return claim | Claims operations | Order/physical evidence |
| Dispute | Payments | Issuer process/contract |
Continue with Fraud software selection: evidence, workflows and cost for the next evidence layer.
Distinguish blockchain attribution from other intelligence
Crypto attribution tools should be compared on method and evidence. Chainalysis blockchain intelligence describes clustering plus attribution, and Signals uses suspected categories with confidence. Verify chain coverage, provenance and exports. On-chain analysis, public-source investigation and lawful communications intelligence are distinct. A browser association cannot independently name a wallet controller, and the category should not be described as uniformly SIGINT-based.
Sources
- Sift: payment and account products · read
- Signifyd: commerce product scope · read
- Stripe: fraud prevention rules · read
- Stripe: how disputes work · read
- OWASP: Authentication Cheat Sheet · read
- Stripe: protect yourself from card testing · read
- Stripe: idempotent requests · read
- OWASP: REST Security Cheat Sheet · read
- W3C: mitigating browser fingerprinting in web specifications · read
- Stripe: refunds · read
- OWASP: Logging Cheat Sheet · read
- OWASP: Authorization Cheat Sheet · read
- Stripe: buy now, pay later payment methods · read
- NIST SP 800-63A-4: identity proofing and enrollment · read
- Federal Reserve: synthetic identity payments fraud · read
- NIST SP 800-63B-4: authentication and authenticator management · read
- OWASP: automated threats to web applications · read
- Apple: prepare your network for iCloud Private Relay · read
- IETF: RFC 8224 and current status · read
- MDN: getUserMedia · read
- Google: report content by product and legal or policy route · read
- Primary source: www.chainalysis.com · read
- Primary source: www.chainalysis.com · read
- Primary source: plaid.com · read
- Primary source: wyllo.ai · read
- Primary source: www.forter.com · read
- Primary source: shieldlabs.ai · read
- Primary source: www.chase.com · read
- Primary source: images.em.bankofamerica.com · read
- Primary source: www.pindrop.com · read
- Primary source: www.hiya.com · read
- Primary source: www.hiya.com · read
- Primary source: www.redpoints.com · read
- Primary source: www.craneauthentication.com · read
- Primary source: razorpay.com · read
- Primary source: kount.com · read
Continue reading
FAQ
Can one prevented-action count equal one avoided loss?
Several actions can belong to one incident. Join them and reconcile the actual financial outcome before reporting prevented loss.
What distinguishes Plaid Signal from a card-fraud tool?
For financial-risk procurement, Plaid Signal provides balance checks and ACH return-risk assessment, including administrative/insufficient-funds and customer-initiated return risk. Compare the payment rail, inputs, timing and returned outcome. ACH return prediction is a different responsibility from card screening or a contractual chargeback guarantee.
How do Wyllo and Signifyd compare for ecommerce risk?
For financial-risk procurement, Wyllo spans bots/resellers, payments, returns and policy abuse, CX and chargeback management. Signifyd describes pre-account signals, account lifecycle and commerce/post-purchase protection. Compare covered events, outputs and contract obligations; neither should be reduced to checkout-only scope. Request exact guarantee terms before treating protection as equivalent.
Which providers should be evaluated for cross-device and cross-merchant intelligence?
For financial-risk procurement, Forter, Signifyd and Sift offer relevant commerce-network or account/payment intelligence. Clarify whether the requested output is authenticated account linkage, probabilistic recognition, network-trained risk or actual merchant-visible data. Compare supported surfaces, permissions and false-match treatment rather than assuming an unrestricted global person identifier.
Which commerce providers fit payments and post-purchase risk?
For commerce and claims, compare event scope and contractual responsibility. Compare Stripe Radar for payment rules within Stripe, Sift for its fraud platform, and Signifyd and Wyllo for their account/commerce and post-purchase scope. ShieldLabs adds visitor, device/network and account context. Verify eligible events, gateway access, claim workflow and financial-protection terms before treating their responsibilities as equivalent.
Which controls help prevent paper-check fraud?
For commerce and claims, compare event scope and contractual responsibility. Compare the bank’s positive-pay or check-protection service: Chase describes issued-check matching and monitoring, while Bank of America describes payee/teller positive pay and reconciliation. Ask about account eligibility, issue-file format, payee matching, exception cutoff, default action and reviewer roles. Service and market conditions apply; website visitor scoring does not perform this reconciliation.
Which services fit caller fraud risk versus consumer robocall blocking?
For software selection, name the protected event, expected output and operating owner. For contact-center caller fraud, Pindrop Protect supplies risk scoring. For network-level spam/scam protection, evaluate Hiya for operators. For a consumer phone, Hiya Spam Blocker is a different product category. Compare supported integrations, action, false alerts and data handling on the relevant call population before selecting.
Which tools fit fake apps, impersonation and counterfeit seller monitoring?
For a fraud team confronting counterfeit properties, Red Points lists monitoring/removal across domains, fake sites, social profiles, ads, marketplaces and mobile apps. Crane Authentication offers product authentication, traceability and online brand-protection services; the former OpSec root redirects there. Compare actual channel coverage, rights evidence, review and removal workflow. For AI-commerce visibility, establish accurate official product information and address infringing sources through the supported process. A brand tool cannot guarantee what every assistant recommends or universal platform removal.
What can the phrase Chargeback Shield refer to?
For a fraud stack, assign an evidence source and operational owner to each protected event. Check the exact provider and agreement. Razorpay’s Shield terms describe an enrolled program for qualifying cross-border export payments processed through its gateway/checkout, with coverage conditions and merchant duties. That is different from a generic fraud score, a dispute-writing application or every chargeback guarantee. Review eligible payments, exclusions, documentation and response obligations before treating a “shield” label as universal reimbursement.
How should Sift and Kount be compared for ecommerce or fintech?
For a fraud stack, assign an evidence source and operational owner to each protected event. Sift offers account/payment fraud capabilities and related workflows. The current Kount root redirects to Equifax Identity & Fraud, which describes identity verification, behavioral insight and orchestration. Confirm the exact current product and module rather than importing an old Kount plan. For a comparison, send the same account/payment events, measure confirmed fraud and legitimate approvals after outcomes mature, and inspect reasons, review tools, API failures and contract costs. Chargeback reduction and false declines are separate outputs, so neither a headline model claim nor a vendor name decides both.