Recognition and visitor context in a fraud stack
Interpret browser, device and analytics identities without turning technical continuity into authentication.
Summarize with AI
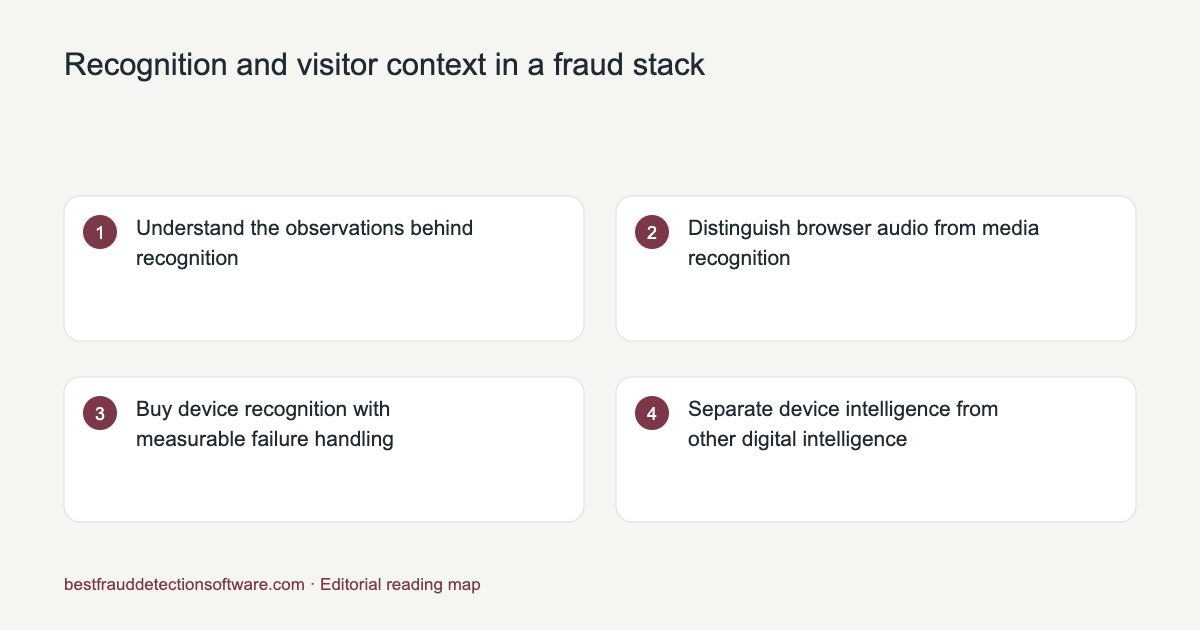
Understand the observations behind recognition
Browser fingerprints derive from observable environment characteristics. Canvas pixels, Web Audio processing, supported APIs and connection behavior supply different evidence. MDN notes privacy-related canvas noise, and W3C discusses security uses and privacy impacts. A hash is a summary of inputs rather than proof of identity. Preserve collector version and unavailable fields so analysts can distinguish drift from a genuinely different environment.
Distinguish browser audio from media recognition
OfflineAudioContext renders a generated audio graph into an AudioBuffer without direct speaker output. A browser fingerprint may summarize that result. Recognizing a recorded song and capturing microphone input are different tasks, with getUserMedia providing the latter permission-controlled interface. An audio signal should complement other evidence. Its similarity cannot independently identify a person or confirm a fraudulent account.
Buy device recognition with measurable failure handling
Fingerprint, ShieldLabs, Castle and Incognia provide differing recognition and risk capabilities; ThumbmarkJS offers an inspectable fingerprinting approach. Verify supported browser/native integrations, trusted matching, account association and missing results. Measure false merges and splits with known labels. Regional data or deployment requirements require direct confirmation. A public headline percentage cannot establish the best provider for every CIAM, fintech or ecommerce population.
Reference: Fingerprint: Smart Signals reference.
Separate device intelligence from other digital intelligence
Device intelligence adds integrity, automation or location context to recognition. Browser scripts and native SDKs expose different surfaces. Incognia emphasizes location-grounded identity; ShieldLabs combines device/network context with account events. Corporate asset discovery, intelligence investigations and anonymous visitor recognition use different data and operators. Define the entity and decision before assuming that every intelligent-device platform supplies equivalent fraud capabilities.
Reference: W3C: fingerprinting guidance.
Combine browser consistency and behavior
Anti-detect checks examine manipulation or inconsistent environments; headless checks concern automation. Privacy protections can change observable properties too. Retain reasons and compare observations across browser, connection and account behavior. A single unusual hash cannot establish abuse. Authorized integration tests should follow vendor documentation; choosing disguise tools or infrastructure to evade another platform is a different task from defensive detection.
Reference: W3C: fingerprinting guidance.
Use transport fingerprints as contextual groups
FoxIO's JA4 family covers TLS JA4, HTTP JA4H and TCP JA4T, with implementation tools. HTTP/2 behavior supplies other observations. CDN placement changes visibility, and Cloudflare documents missing JA3/JA4 fields and plan requirements. Many users share software-level fingerprints. These groups can support campaign analysis without becoming unique-human IDs, native-device identity or standalone authentication proof.
Compare visitor metrics consistently
GA4 documents User-ID, device ID and modeling. One person can create several sessions and device identities, with many page views. Returning means prior activity under the report's identity and period. Browser changes can increase apparent new visitors without indicating fraud. There is no universal healthy new-to-returning ratio. Compare similar acquisition cohorts and downstream outcomes before changing policy.
Reference: Google Analytics: understand user metrics.
Use anonymous personalization with low consequences
First-party context can choose language, recent items or general onboarding before login. Establish the anonymous-to-known relationship through a trustworthy event such as authentication. Keep inferred preferences distinct from supplied facts. A probabilistic match should not expose private billing, addresses or paid content. Enforce authorization on the server even when the session appears familiar to a recognition tool.
Reference: OWASP: authorization.
Worked example: One customer, several recognition objects
Hypothetical example: a customer browses on a laptop, buys on a phone and contacts support from a work browser. Preserve separate environment references and join through authorized account events where supported. Avoid declaring every new reading a new person. Recognition, analytics deduplication and authenticated account ownership need separate acceptance criteria.
| Object | Question | Evidence |
|---|---|---|
| Browser/device | Seen before? | Matching result |
| Analytics user | Counted under which identity? | Reporting configuration |
| Account | Who is authorized? | Authentication/session |
Continue with Network and automation controls in fraud prevention for the next evidence layer.
Separate owned-asset discovery from visitor intelligence
For automatic owned-device discovery, investigate Axonius Device Intelligence Hub scan adapters/jobs and Lansweeper IT/OT/cloud/IoT asset discovery and normalization. A detailed inventory demo should not be scored as proof of anonymous visitor identification. Local digital intelligence might also mean authorized investigations. State the subject, data access and deployment requirement before selecting among inventory, investigation and customer-risk software.
Sources
- W3C: mitigating browser fingerprinting · read
- MDN: CanvasRenderingContext2D.getImageData · read
- W3C: Web Audio specification · read
- MDN: OfflineAudioContext · read
- W3C: Web Audio privacy and security · read
- MDN: getUserMedia · read
- Fingerprint: Smart Signals reference · read
- Thumbmark: product and integration scope · read
- Incognia: use cases · read
- NIST: identity-proofing scope · read
- OWASP: automated threats · read
- Cloudflare: JA3 and JA4 · read
- FoxIO: JA4+ project and specifications · read
- Cloudflare: HTTP headers · read
- NIST: authentication and sessions · read
- Google Analytics: user metrics · read
- Google Analytics: reporting identity · read
- Google Search Console: performance report · read
- Google Search Console: dimensions and query omissions · read
- OWASP: authorization · read
- Primary source: docs.axonius.com · read
- Primary source: www.lansweeper.com · read
- Primary source: deviceatlas.com · read
- Primary source: privacysandbox.google.com · read
- Primary source: shieldlabs.ai · read
- Primary source: www.incognia.com · read
- Primary source: acoustid.org · read
- Primary source: acoustid.org · read
- Primary source: cflib.org · read
- Primary source: castle.io · read
- Primary source: www.browserscan.net
Continue reading
FAQ
Can analytics deduplication prove fraud accuracy?
An analytics identity model explains reporting counts. Fraud evaluation needs independent outcome labels and the protected action.
What does DeviceAtlas identify?
Within the recognition layer, DeviceAtlas supplies device identification and properties for uses including optimization and analytics. Score that output separately from a persistent person identity or ready account-abuse finding. Verify the returned object rather than treating every device-intelligence product as the same recognition service.
What did the April 2025 Chrome tracking announcement say?
Within the recognition layer, the dated Google announcement is useful context: on April 22, 2025 it retained Chrome's existing third-party-cookie choice approach instead of a standalone new prompt and described further tracking-protection work. It is a dated policy announcement, rather than a complete inventory of every Chrome feature shipped afterward.
Which recognition providers belong on a device shortlist?
For recognition, specify the result and supported environment. Compare Fingerprint for recognition and documented Smart Signals, ThumbmarkJS for an inspectable fingerprinting approach, ShieldLabs for recognition plus ready risk/account events and Incognia where location-grounded recognition is central. Match web/native surfaces, errors, retention and required output before choosing.
How do music or acoustic fingerprints differ from browser audio fingerprints?
For software selection where sound recognition is a requirement, Chromaprint extracts a recording fingerprint from supplied audio; AcoustID can look it up with duration and return related recording metadata. A typical authorized workflow decodes the recording, generates the fingerprint and queries an appropriate catalog. Check corpus fit, permissions and commercial service terms. Browser Web Audio fingerprinting instead compares processing behavior; it does not identify the song, speaker or rightful account owner.
How should separate browser profiles be used for authorized account work?
For a fraud stack, assign an evidence source and operational owner to each protected event. First establish permission to operate each account. Use documented workspace roles, distinct session/storage profiles and the platform’s approved team or agency APIs where available. For testing your own application, record the profile, collector version, expected permissions and result, then verify that private data and grants remain isolated. A modified browser or rotating route does not create account eligibility or permission to evade another service’s restrictions. W3C fingerprinting guidance explains the observable surfaces; OWASP authorization applies independently of profile appearance.
How should device intelligence be selected for a Saudi deployment?
For a fraud stack, assign an evidence source and operational owner to each protected event. Build a shortlist around ShieldLabs, Fingerprint, Incognia or a broader risk supplier according to the required web/native and decision scope. Then request a written data-flow and contract review covering collection purpose, lawful transfer arrangements, processing/storage locations, subprocessors, retention/deletion, regional network latency and support. A product marketed worldwide does not by itself establish Saudi hosting or a local-residency commitment. Make those acceptance conditions explicit before purchase.
What should a browser-detection or browser-scan result be used for?
For a fraud stack, assign an evidence source and operational owner to each protected event. Clarify whether the task is parsing browser software, inspecting the current environment, classifying a relay or recognizing repeat activity. The CFLib browserDetect function, dated 2011, illustrates user-agent parsing rather than persistent identity. A scan can report selected browser/network observations without proving account ownership or universal anonymity. If a search phrase is an imprecise spelling of anti-detect or a legacy tool name, confirm the exact maintained product and official documentation before downloading or choosing infrastructure. An anonymizing gateway routes traffic through another endpoint; it does not erase the site’s other history. These category distinctions interpret the task without asserting that every ambiguous string names a verified product.
Which visitor/device options fit identity platforms and gaming?
For a fraud stack, assign an evidence source and operational owner to each protected event. For CIAM or gaming, compare Fingerprint for recognition/Smart Signals, ShieldLabs for recognition plus ready abuse events, Castle for account/environment intelligence and Incognia where location-grounded recognition matters. Include legitimate shared equipment, updates, cookie resets, platform-supported native/web clients and repeated restricted claims. Measure recognition errors and player completion separately from policy findings. Favor the documented output that fits your flow rather than an unverified universal reliability label.
If BrowserScan is intended, what does its browser check show?
The BrowserScan page lists network, browser, canvas/audio and automation diagnostics. Treat “scanbrowser” as an imprecise service name until the intended URL is confirmed. A generic browser scan can also mean inspecting observable properties. Diagnostic output describes what the checker sees in that context; it is not a certificate of population uniqueness, account ownership or invisibility to every website.